Enterprise Data Governance, Information Protection & DLP Explained Simply & Executed Flawlessly
Shield Data Partners helps global enterprises discover their dark data, build custom sensitivity taxonomies, automate auto-labeling policies, and prevent data loss across hybrid clouds—without disrupting daily business operations.
🛡 Purview Governance & Protection Suite
How to Make Sense of Enterprise Data Governance & Security
When we speak with CIOs, CDOs, and CISOs, we hear the same frustration: data is sprawling across Azure, Microsoft Fabric, AWS, Snowflake, and on-premises legacy servers. Nobody has a single source of truth for where sensitive customer records live, compliance audits cause weeks of fire drills, and security rules frequently trigger false alarms that block regular employees from doing their jobs.
Microsoft Purview solves these challenges when architected correctly. But it requires treating Governance, Classification, and Data Loss Prevention as three interconnected gears:
- 1. Governance tells you what you have: It automatically catalogs all your hybrid data sources, traces end-to-end lineage from ingestion to Power BI, and assigns verified business owners so teams can trust their data.
- 2. Information Protection ensures security travels with the data: It doesn't rely on generic labels or manual user tagging. We build custom label taxonomies tailored to your departments, train AI classifiers on your actual documents, and configure auto-labeling policies so protection happens automatically in the background.
- 3. DLP stops sensitive data from walking out the door: It prevents confidential files from being copied to USB drives, personal clouds, or external chats—rolled out safely in silent simulation mode so your business never experiences disruption.
Below, we detail exactly what we do and why global enterprises choose Shield Data Partners to lead their Purview implementations.
Things We Can Do with Microsoft Purview
We break down the complexity of Microsoft Purview into three clear, production-ready capabilities. Here is exactly what we architect, configure, and manage for your organization.
1. Enterprise Data Governance & Unified Catalog
Discover, catalog, trace lineage, and govern multi-cloud and enterprise data assets.
Automated Multi-Cloud Scanning
We configure automated, scheduled off-peak metadata scans across your hybrid estate without exposing credentials or crossing unencrypted public routes.
- Managed Virtual Network (VNet) Private Endpoints
- Self-Hosted Integration Runtime (SHIR) clusters
- Azure Key Vault Managed Identity secret rotation
- Zero disruption to transactional database workloads
End-to-End Automated Lineage
We give you full transparency into how data moves from raw ingestion to executive dashboards, accelerating audit readiness and root-cause analysis.
- Azure Data Factory (ADF) & Synapse pipeline tracing
- Microsoft Fabric OneLake, Lakehouse & Warehouse lineage
- Automated Power BI semantic model dependency maps
- Upstream impact analysis for planned schema changes
Business Glossary & Stewardship
We bridge business and engineering teams with verified enterprise definitions, ownership assignments, and data quality scoring.
- Hierarchical enterprise business glossary creation
- Mapping Critical Data Elements (CDEs) to physical tables
- Domain-based data mesh modeling and curation
- Collection-level Role-Based Access Control (RBAC)
2. Information Protection, Custom Taxonomies & Auto-Labeling
Bespoke label taxonomies, machine learning classifiers, and automated policies across emails, files, and cloud stores.
Custom SITs & Exact Data Match
We eliminate regex false alarms by matching actual database records against cryptographic, salted SHA-256 hashes without exposing raw plaintext.
- Custom SIT regex + proximity keyword dictionaries
- Salted SHA-256 hashes of client database tables
- Multi-token verification (Name + National ID + Account)
- Zero false positives on high-volume customer PII/PCI
Trainable Classifiers (ML)
We train supervised machine learning models on your actual documents to automatically categorize unstructured files that lack rigid regex formats.
- Trained on positive and negative client document corpuses
- Classifies contracts, NDA agreements, and IP patents
- Categorizes software source code and financial disclosures
- High precision scoring tuned to eliminate false detections
Bespoke Label Taxonomies
We don't limit you to standard generic tiers. We design custom multi-level label hierarchies and sub-labels mapped to your exact organization structure.
- Tailored sub-labels (e.g. Confidential \ Finance, Legal, HR)
- Regulatory tags: Restricted \ Patient PHI, ITAR, Banking
- Azure RMS encryption with scoped user/group permissions
- Dynamic visual headers, footers & container protection
Automated Auto-Labeling Policies
We eliminate human error by configuring automated labeling rules that evaluate content and apply persistent protection automatically.
- Client-Side: Recommended / Mandatory in Word, Excel, Outlook
- Server-Side: Automated at-rest scanning across M365 & Fabric
- Safe Simulation Mode to audit matches before enforcement
- Protects Exchange mailboxes, SharePoint & OneDrive at scale
3. Data Loss Prevention (DLP) & Incident Triage
Prevent unauthorized data exfiltration across endpoints, email, chat, and cloud shares with zero business disruption.
Endpoint DLP (Windows & macOS)
We safeguard corporate laptops and workstations against unauthorized local transfers, personal cloud uploads, and physical exfiltration.
- USB mass storage read-only enforcement or blocking
- Restricting unapproved personal cloud sync (Dropbox, Drive)
- Clipboard copy/paste and screen capture auditing
- Print restriction and unmanaged network share protection
M365 & Multi-Channel Collaboration DLP
We inspect content in flight across email, chat, and document collaboration tools, catching accidental data exposure before it leaves the organization.
- Exchange Online automatic message encryption or external block
- Teams chat and channel real-time sensitive card blocking
- SharePoint & OneDrive anonymous link revocation
- Fabric & Power BI semantic model DLP policy rules
Phased Rollout & SOC Incident Triage
We deploy policies safely through a proven 4-stage rollout framework backed by operational alert triage and Microsoft Sentinel integration.
- Stage 1: Silent Audit & Simulation (0 user impact)
- Stage 2: In-app educational Policy Tips
- Stage 3: Justification-based overrides → Stage 4: Full Block
- Purview Alert Dashboard triage & SOC escalation runbooks
Why Partner with Shield Data Partners?
Choosing a consulting partner for enterprise data governance and security is a major decision. Here is why multinational enterprises, financial institutions, and healthcare providers trust Shield Data Partners over generalist IT vendors.
Deep Purview Specialization, Not Generalist IT
Many IT consulting firms treat Microsoft Purview as a sideline to generic cloud migrations or web development. We are a specialized Center of Excellence (CoE) dedicated 100% to Microsoft Purview, Microsoft Fabric Governance, and Data Loss Prevention. You get senior architects who live and breathe this technology daily.
Bespoke Taxonomies & Trainable Classifiers
Standard implementations frequently fail because they try to force an organization into four rigid default labels that employees don't understand. We design custom multi-level label hierarchies mapped to your actual business units (Finance, HR, Legal, R&D) and train custom machine learning models on your real-world contracts and files.
Automated Auto-Labeling, Zero Human Error
Relying on busy employees to remember to tag sensitive files is the number one cause of data leaks. We configure smart in-app recommendations in Office apps and automated background server-side policies across Exchange, SharePoint, OneDrive, and Fabric so your data is protected automatically without relying on user memory.
Zero-Disruption Phased Simulation Rollout
Nothing destroys a data protection initiative faster than heavy-handed DLP rules that break business operations on day one. We follow a strict 4-stage adoption methodology: silent simulation first to review match data, friendly in-app policy tips to guide employees, and only enforcing blocks once accuracy is 100% verified.
100% In-Tenant Remote Isolation Guarantee
As an international IT consulting export practice, security and confidentiality are foundational. Our architects and engineers operate strictly inside your designated Azure tenant using Azure Bastion, Privileged Identity Management (PIM), and multi-factor authentication. Zero customer data ever leaves your tenant boundaries.
Fast-Track ROI with Transparent SLAs
We eliminate endless consulting engagements that drag on for quarters with vague milestones. Whether you engage our 4-Week Fast-Track Accelerator, a dedicated offshore CoE pod, or 24/7 managed alert triage, you receive clear scope definitions, transparent fixed pricing, and rapid measurable compliance outcomes.
Supported Enterprise Data Sources
Microsoft Purview goes far beyond native Azure. Our engineers configure seamless scanning, auto-labeling, and metadata extraction across your entire hybrid, multi-cloud, and SaaS estate.
Azure & Modern Data
- Azure SQL DB & Managed Instances
- Azure Data Lake Storage (ADLS Gen2)
- Azure Synapse Analytics (Dedicated & Serverless)
- Azure Cosmos DB (NoSQL & MongoDB)
- Azure Blob Storage & Files
Microsoft Fabric
- Fabric OneLake Lakehouses & Warehouses
- Fabric Mirrored Databases (Snowflake, Cosmos)
- Power BI Semantic Models & Reports
- Fabric Real-Time Analytics & KQL DBs
- Fabric Workspace Governance & RBAC
Cross-Cloud Estates
- Amazon Web Services (AWS S3 & RDS)
- Snowflake Data Cloud (Multi-region)
- Databricks Unity Catalog & Delta Tables
- Google Cloud Platform (BigQuery & Cloud Storage)
- Apache Kafka & Hive Metastore
Core Enterprise Systems
- Microsoft SQL Server (2012–2022 via SHIR)
- Oracle Database & Teradata Systems
- SAP S/4HANA & SAP ECC
- PostgreSQL, MySQL & DB2
- Salesforce, ServiceNow & Microsoft 365
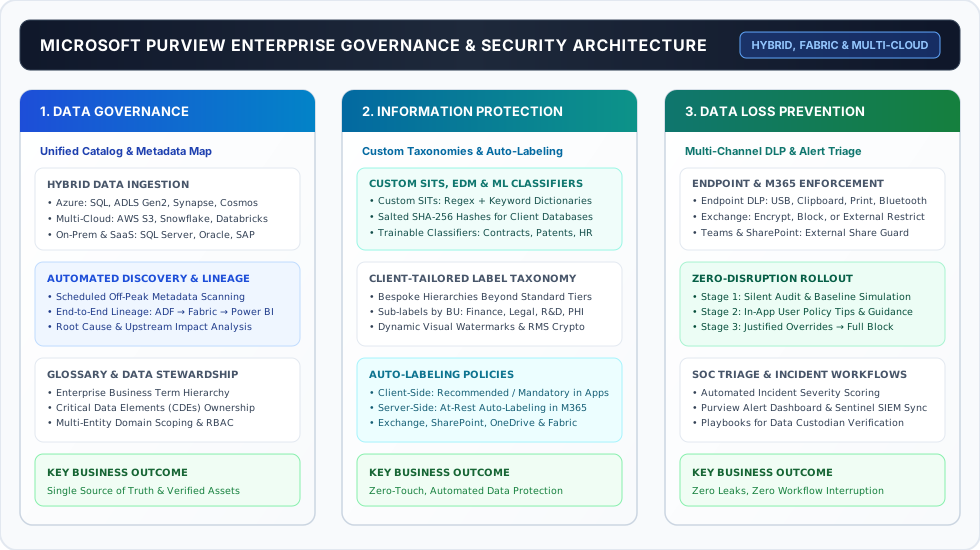
Enterprise Purview Architecture Blueprint
A comprehensive reference architecture demonstrating how Purview orchestrates multi-cloud governance, custom ML classifiers, automated auto-labeling, and cross-channel DLP.
How Enterprises Work with Us
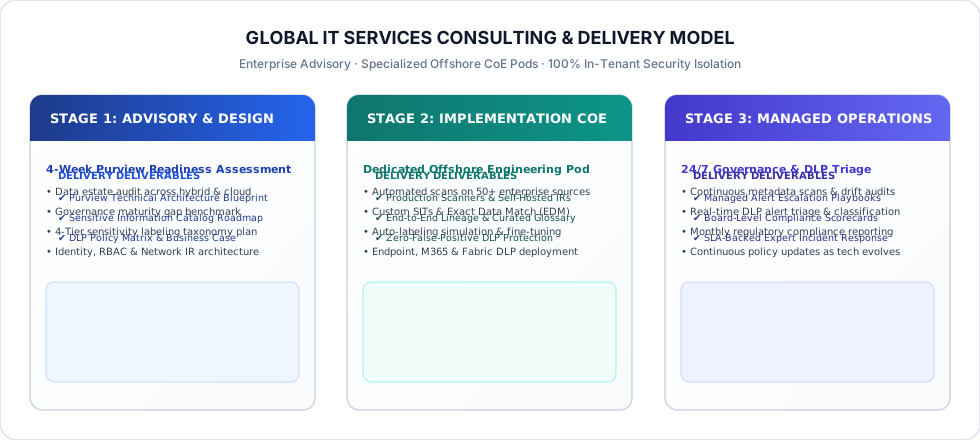
Whether you require a rapid 4-week accelerator, a dedicated offshore engineering pod, or 24/7 managed governance operations, we offer tailored models with transparent SLAs and strict security guarantees.
4-Week Purview Foundation
Ideal for enterprises seeking rapid baseline visibility, tenant readiness verification, custom sensitivity label taxonomy design, and initial auto-labeling pilot.
- Tenant readiness & network private endpoint setup
- Baseline scanning across 5 core enterprise sources
- Bespoke sensitivity label hierarchy & sub-label design
- Initial auto-labeling policy simulation across pilot sites
- Executive maturity scorecard & rollout business case
Dedicated CoE Pod
A dedicated team of certified Purview architects, DLP engineers, and metadata curators executing full multi-cloud scanning, ML trainable classifiers, EDM, and auto-labeling policies.
- Full multi-cloud scanning across 30+ hybrid data sources
- Custom SITs & Exact Data Match (EDM) salted hashing
- Machine Learning Trainable Classifiers for complex files
- Client-side & server-side auto-labeling policy rollout
- Endpoint DLP (USB, Cloud, Print) & M365 Collaboration DLP
Managed CoE & Alert Triage
Ongoing operational management for enterprise data catalogs, recurring scan scheduling, metadata drift audits, auto-labeling rule maintenance, and real-time DLP alert triage.
- Continuous metadata scanning & schema drift monitoring
- Periodic re-training of ML classifiers as documents evolve
- Real-time DLP alert triage & incident severity scoring
- Monthly executive compliance & auto-labeling scorecards
- Quarterly regulatory audits (GDPR, HIPAA, DPDP)
Our Consulting & Delivery Methodology
A structured, risk-mitigated approach honed across complex enterprise rollouts to ensure high adoption and zero disruption.
Assess & Discover
Evaluate current data governance maturity, identify dark data blind spots, and map regulatory requirements (GDPR, HIPAA, PCI-DSS, DPDP).
- Data estate inventory audit
- Regulatory compliance mapping
- Identity & RBAC evaluation
- Architecture blueprint definition
Architect & Design
Design the Purview collection topology, bespoke sensitivity taxonomy, custom SIT regex dictionaries, and ML trainable classifier sample corpuses.
- Client-tailored label hierarchies
- Trainable classifier sample curation
- EDM database schema mapping
- Auto-labeling simulation rules
Implement & Pilot
Deploy automated scanners, train ML classifiers, upload salted EDM hashes, and test auto-labeling policies in safe simulation mode.
- Automated scanner rollout
- ML classifier training & testing
- Server-side auto-labeling simulation
- DLP policy simulation & tuning
Enforce & Manage
Enforce in-app and at-rest auto-labeling, activate DLP policy tips and blocking, establish SOC alert triage playbooks, and ensure ongoing governance.
- Full auto-labeling enforcement
- DLP blocking & quarantine
- SOC alert triage integration
- Ongoing metadata drift audits
Measurable Enterprise Impact
See how global enterprises leverage Shield Data Partners to protect sensitive data, eliminate false alarms, and streamline compliance.
Zero-False-Positive EDM & Auto-Labeling for 45M Records
A multinational financial institution faced thousands of daily false alarms and unclassified legacy file shares containing high-risk financial data.
Trainable Classifiers & Custom PHI Labels Across Hybrid Systems
A healthcare network required automated detection for non-standardized doctor diagnostic summaries, clinical trials, and patient PHI across cloud lakes.
Multi-Collection Data Mesh & Cross-Tenant Auto-Labeling
A diversified industrial corporation required standardized data governance and IP protection across three independent subsidiary entities sharing Fabric OneLake.
Request an Architecture Review or RFP Proposal
Connect directly with our Microsoft Purview & Data Governance Solutions Architects. We will assess your environment, review custom label and auto-labeling requirements, and deliver a tailored implementation roadmap.
- Direct consultation with Principal Purview Architects
- Bespoke sensitivity label taxonomies & sub-labels
- Custom SITs, Trainable Classifiers & Auto-Labeling
- Confidential NDA protection for all tenant discussions
- Transparent fixed-price or dedicated pod pricing